Decentralized networks face a unique set of challenges when it comes to security, with the Sybil attack crypto being one of the most insidious threats. This type of attack involves a single entity creating multiple fake identities or nodes to gain disproportionate influence over the network. Understanding how these distributed systems defend against such sophisticated assaults is crucial for anyone engaging with blockchain technology or other peer-to-peer environments.
Successfully combating a Sybil attack ensures the integrity of consensus mechanisms, preventing malicious actors from subverting the network’s operations. Without robust defenses, a decentralized network could fall prey to censorship, transaction manipulation, or even a complete takeover, undermining its core principles of trustlessness and decentralization.
Key Takeaways
- A Sybil attack involves a single attacker controlling numerous identities to dominate a decentralized network.
- Proof-of-Work (PoW) deters Sybil attacks by requiring significant computational resources, making it costly to control a majority.
- Proof-of-Stake (PoS) uses economic disincentives, such as staking requirements and slashing, to prevent malicious behavior.
- Emerging defenses include decentralized identity systems and network-layer analysis to detect and isolate fake nodes.
- Hybrid consensus models and AI-driven anomaly detection are evolving to counter increasingly sophisticated Sybil attack crypto vectors.
Understanding the Sybil Attack Crypto Threat
The Sybil attack represents a fundamental challenge to the security and integrity of decentralized systems. In essence, it’s an attempt by a single malicious actor to control a large number of identities or nodes within a network, thereby disrupting its normal operations or gaining undue influence. This can manifest in various ways, from preventing legitimate transactions to manipulating the network’s consensus process.
For instance, if an attacker controls a majority of nodes, they could potentially censor transactions, double-spend cryptocurrencies, or even rewrite parts of the blockchain’s history. This threat is particularly potent in peer-to-peer networks where participants are often anonymous and trust is distributed rather than centralized. The underlying principle of decentralization, which seeks to eliminate single points of failure, paradoxically creates a vulnerability to this kind of attack if not properly mitigated.
Anatomy of a Sybil Attack
A Sybil attack operates by exploiting the anonymity and low cost of identity creation within many decentralized systems. The attacker generates numerous pseudonymous identities, each appearing as an independent node to the rest of the network. These fake identities then participate in network operations, such as relaying messages, validating transactions, or voting on governance proposals.
The goal is to achieve a numerical advantage, allowing the attacker to sway decisions or monopolize network resources. For example, in a distributed ledger technology (DLT) network, a Sybil attacker might create hundreds or thousands of nodes that all vote in unison, effectively overriding the legitimate participants. This can lead to a compromise of the network’s integrity and a loss of trust among its users. The ease with which these identities can be forged without significant cost is what makes the Sybil attack crypto threat so pervasive.
Why Decentralized Systems are Vulnerable
Decentralized systems inherently rely on open participation and the absence of a central authority to verify identities. While this design fosters censorship resistance and inclusivity, it also opens the door to Sybil attacks. Traditional centralized systems often use KYC (Know Your Customer) or other verification processes to link identities to real-world individuals, making it harder to create multiple fake accounts. In a blockchain context, where pseudonyminity is often a feature, such verification is deliberately avoided.
Furthermore, many decentralized networks operate on consensus mechanisms that assume a majority of participants are honest. If a Sybil attacker can accumulate enough fake identities to constitute this majority, they can undermine the very foundation of the network’s security. This is particularly relevant for smaller or newer blockchain projects that might have fewer legitimate nodes, making them easier targets for a determined attacker. The challenge lies in creating a system that allows open participation while simultaneously making it prohibitively expensive or difficult to forge multiple identities.
Proof-of-Work (PoW): A Foundation Against Sybil Attacks
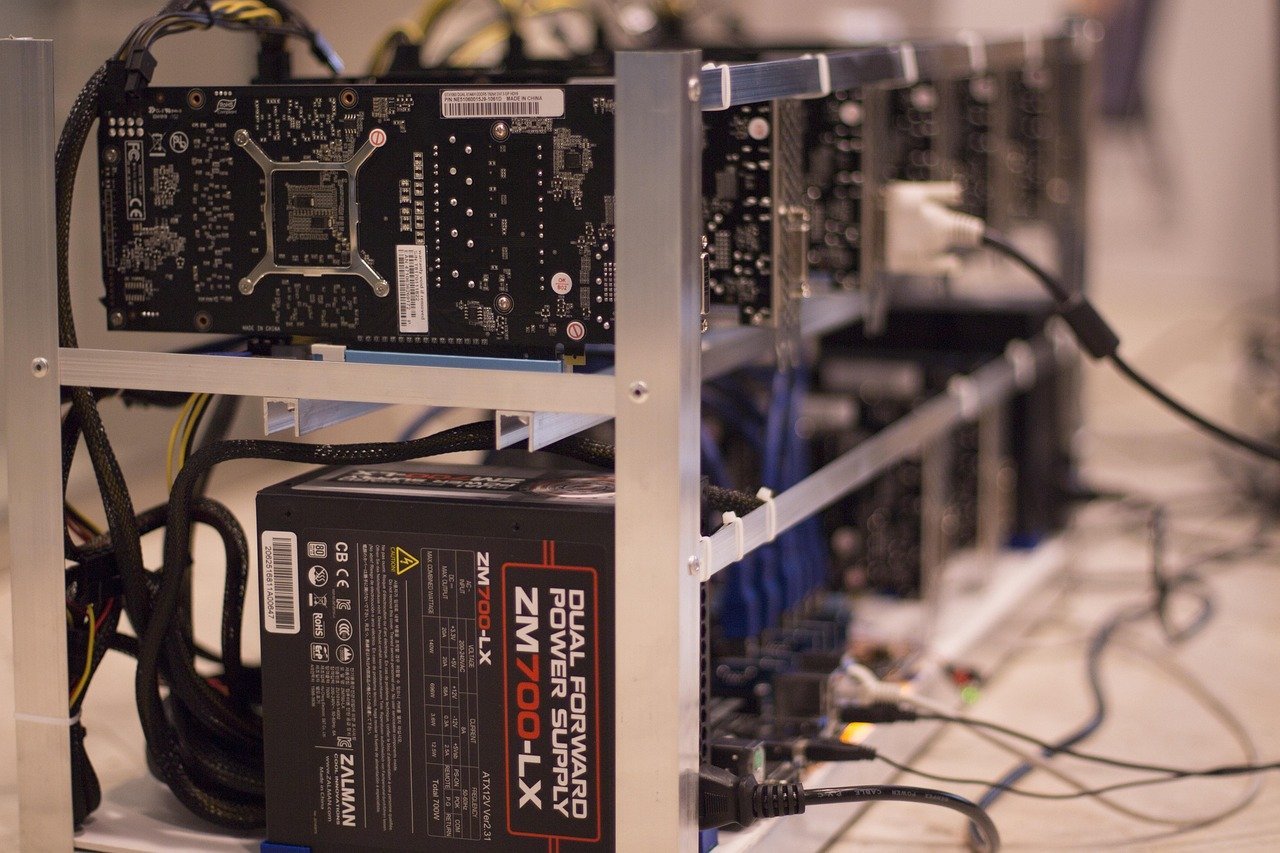
Proof-of-Work (PoW) is arguably the most well-known and battle-tested defense mechanism against Sybil attack crypto, primarily exemplified by Bitcoin. The core principle of PoW is to make it computationally expensive to create a new block and participate in the network’s consensus. This computational cost acts as a strong deterrent against a Sybil attack because controlling a significant portion of the network’s hashing power requires immense financial investment in hardware and electricity.
In a PoW system, nodes (miners) compete to solve a complex cryptographic puzzle. The first miner to solve it gets to add the next block to the blockchain and receives a reward. This process is inherently resource-intensive. A Sybil attacker would need to acquire a vast amount of mining equipment and consume enormous amounts of energy to generate enough hashing power to overcome the legitimate miners. This economic barrier makes it extremely difficult for a single entity to gain a controlling majority (e.g., a 51% attack), as the operational costs would quickly become unsustainable. Bitcoin’s network, for instance, has successfully resisted numerous attempts at such an attack due to its vast, distributed hashing power, making any single entity’s takeover prohibitively expensive.
Bitcoin’s Defense Mechanism
Bitcoin’s PoW mechanism, often referred to as ‘Nakamoto Consensus,’ ensures that adding new blocks to the chain requires a significant amount of ‘work.’ This work is measured by the computational effort spent on finding a valid hash. The difficulty of this puzzle adjusts over time, ensuring that blocks are found approximately every ten minutes, regardless of the total hashing power on the network. This continuous difficulty adjustment means that even if a Sybil attacker brings online a large number of fake nodes, the difficulty will increase, making it harder for them to maintain a dominant share of the hashing power without exponential increases in investment.
The economic incentives of Bitcoin also play a crucial role. Honest miners are rewarded with newly minted bitcoins and transaction fees, motivating them to maintain the network’s integrity. A successful Sybil attack, leading to a loss of trust and a collapse in Bitcoin’s value, would ultimately destroy the very assets the attacker sought to control, thus eliminating their potential profit. This self-reinforcing economic model makes Bitcoin remarkably resilient to malicious manipulation.
Limitations and Energy Consumption
While effective, PoW is not without its limitations, especially concerning environmental impact and scalability. The immense computational power required to secure networks like Bitcoin translates into substantial energy consumption. As of 2026, the global energy consumption for Bitcoin mining is projected to be equivalent to that of a mid-sized country, raising significant environmental concerns. This high energy cost, while a deterrent for attackers, is also a constant overhead for the network, leading to discussions about more energy-efficient alternatives.
Furthermore, the ‘arms race’ in mining hardware can lead to centralization of mining power among a few large pools or entities that can afford the latest, most efficient Application-Specific Integrated Circuits (ASICs). While not strictly a Sybil attack, this concentration could theoretically lead to a 51% attack if one entity gains control over a majority of the hashing power. For instance, if a nation-state or a consortium of powerful mining pools were to collude, they could theoretically orchestrate such an attack, despite the enormous costs involved. This potential for centralization in mining distribution remains a point of debate and active research in the blockchain community.
Proof-of-Stake (PoS): Economic Deterrents for Sybil Attack Crypto
Proof-of-Stake (PoS) offers an alternative approach to defending against a Sybil attack crypto, shifting the focus from computational power to economic stake. In a PoS system, validators (analogous to miners in PoW) are chosen to create new blocks based on the amount of cryptocurrency they have ‘staked’ as collateral. The more tokens a validator stakes, the higher their chance of being selected to validate transactions and earn rewards. This mechanism directly addresses the Sybil problem by requiring a significant economic commitment from each participant.
Unlike PoW, where an attacker needs to invest in expensive hardware and electricity, a PoS attacker would need to acquire a substantial portion of the network’s native tokens. To launch a 51% attack, an attacker would need to control 51% of the total staked tokens, which for large networks like Ethereum 2.0, represents an astronomical sum. As of early 2026, acquiring 51% of staked ETH could easily cost hundreds of billions of dollars, making such an endeavor economically unfeasible and highly risky. The fundamental idea is that any entity holding such a large stake would be incentivized to act honestly, as a successful attack would devalue their own holdings, leading to massive financial losses.
Staking as a Sybil Defense
The act of staking tokens serves as the primary defense against Sybil attacks in a PoS network. By requiring validators to lock up a significant amount of capital, the system creates a strong economic barrier to entry for malicious actors. Each staked token represents a ‘vote’ or influence in the network, so to gain a controlling influence, an attacker must acquire and stake a majority of the network’s tokens. This makes it far more expensive than simply creating numerous low-cost identities.
Consider networks like Cardano or Solana. To become a significant validator on these networks requires a substantial investment in their respective native tokens. Even if an attacker were to acquire enough tokens, they would then be financially incentivized to maintain the network’s health to protect their own investment. Any action that damages the network’s reputation or security would directly lead to a decrease in the value of their staked assets, ensuring their self-interest aligns with the network’s well-being. This alignment of incentives is a cornerstone of PoS security model.
Slashing Mechanisms and Penalties
Beyond the initial staking requirement, PoS systems often incorporate ‘slashing’ mechanisms. Slashing is a punitive measure where a portion of a validator’s staked tokens is automatically removed or ‘slashed’ if they engage in malicious behavior, such as double-signing transactions, being offline for extended periods, or colluding in an attack. This acts as a powerful economic disincentive, making the potential financial losses for attempting a Sybil attack extremely high.
For instance, Ethereum 2.0 has specific slashing conditions for validators caught violating network rules. The penalties can range from a small percentage of their stake for minor infractions to a significant portion for severe offenses. This risk of financial loss, combined with the high cost of acquiring a majority stake, makes PoS networks highly resistant to Sybil attacks. The transparent nature of blockchain also allows the network to identify and penalize dishonest validators efficiently, further reinforcing the security posture of the distributed ledger technology.
Identity and Reputation Systems: Beyond Pure Consensus
While PoW and PoS primarily rely on computational or economic costs to deter Sybil attacks, another class of defenses explores identity and reputation systems. These methods aim to link network identities to a verifiable, scarce resource or a web of trust, making it difficult for a single entity to masquerade as many. These approaches are often more experimental and less widely adopted in major public blockchains but hold promise for specific applications or private consortium blockchains.
The fundamental challenge here is balancing decentralization and privacy with the need for Sybil resistance. If identities are too easily verifiable, it could lead to centralization or compromise user privacy. However, a carefully constructed identity layer can add a crucial dimension of security. Projects are exploring ways to assign unique, cryptographically secured identifiers to participants, or to establish reputation scores that accumulate over time based on honest participation, making new, unverified identities less influential.
Decentralized Identity Solutions
Decentralized Identity (DID) solutions seek to create unique, self-sovereign digital identities that are controlled by the user, not a central authority. These identities can be cryptographically linked to real-world attributes or verifiable credentials without revealing personal information directly on the blockchain. For example, a DID system might allow a user to prove they are over 18 without revealing their exact birthdate, or prove they are a unique human without disclosing their government ID.
Projects like Worldcoin (with its iris scanning) or Ethereum-based identity protocols are experimenting with various methods to ensure ‘proof of personhood’ – that a user is a unique human and not a bot or a Sybil account. By requiring a unique, non-duplicable attribute (like a biometric scan or a verified social graph connection), these systems make it significantly harder for an attacker to create multiple fake identities. This can be especially useful in decentralized autonomous organizations (DAOs) where one-person-one-vote models are desired.
Web-of-Trust and Social Graph Validation
Another approach to combat the Sybil attack crypto problem is through web-of-trust models and social graph validation. Instead of a single, central authority, trust is established through a network of interconnected users who vouch for each other’s identities. If a new node joins the network, its trustworthiness is assessed based on its connections to already trusted nodes.
For instance, some decentralized social networks might give more weight to posts or governance votes from users who are connected to a certain number of other users who themselves have a good reputation. This creates a social cost for creating fake identities, as they would need to painstakingly build a network of trusted connections, which is time-consuming and difficult to fake at scale. Graph analysis algorithms can be employed to detect suspicious patterns, such as multiple new identities connecting to a single existing identity, which could indicate a Sybil cluster. The effectiveness of this method heavily relies on the initial seeding of trust and the community’s vigilance in identifying and isolating malicious actors.
Network Layer Defenses and Advanced Techniques
Beyond the consensus mechanism and identity layers, decentralized networks also employ defenses at the network layer itself. These techniques focus on analyzing the communication patterns and topological structure of the peer-to-peer network to identify and isolate Sybil nodes. By understanding how nodes connect and interact, it’s possible to detect anomalous behavior that suggests a single entity is controlling multiple pseudonyms.
These defenses often work in conjunction with other mechanisms. For example, even if an attacker manages to acquire some stake in a PoS network, network-layer analysis might still flag their multiple nodes as suspicious if they exhibit unusual communication patterns or appear to be centrally controlled. This multi-layered approach provides a more robust defense, making it harder for Sybil attackers to exploit any single vulnerability. The sophistication of these techniques continues to evolve, incorporating elements of machine learning and graph theory to identify subtle signs of attack.
Detecting Malicious Nodes
Detecting malicious nodes often involves sophisticated network monitoring and analysis. One common technique is to analyze the latency and connectivity patterns of nodes. If multiple nodes consistently exhibit identical or highly correlated network behavior (e.g., responding at the exact same time, having identical IP addresses in different parts of the world, or always relaying messages in a specific, non-random sequence), it could indicate they are controlled by the same entity. Graph-based algorithms can map the network’s topology and identify clusters of nodes that are unusually interconnected or originate from a single entry point.
For example, researchers have developed methods to analyze the Bitcoin network’s P2P layer to estimate the number of unique IP addresses and identify potential Sybil nodes by looking for nodes that share the same underlying network infrastructure. This kind of traffic analysis, while challenging due to encryption and relays, can provide valuable clues. Furthermore, some systems might introduce random delays or require specific cryptographic challenges to verify node uniqueness, making it harder for a Sybil attacker to automate consistent, seemingly independent responses from their fake nodes. The ongoing arms race between attackers and defenders necessitates constant innovation in detection methods.
Sybil Resistance in Private Blockchains
While public, permissionless blockchains face the greatest challenges from Sybil attacks due to their open nature, private or permissioned blockchains also implement Sybil resistance, albeit through different means. In these environments, participants are typically pre-approved and known entities, often corporations or consortia. The ‘identity’ of each node is therefore explicitly managed and verified off-chain.
For instance, a consortium blockchain used by banks for interbank settlements would have a strict whitelist of approved participants. Each bank would operate a single, verified node, and any attempt to introduce additional, unapproved nodes would be immediately detected and rejected. The Sybil attack crypto threat is mitigated through centralized access control and a strong underlying trust framework among known participants. However, this comes at the cost of sacrificing some decentralization compared to public blockchains. The choice between permissionless and permissioned approaches often depends on the specific use case and the desired balance between security, privacy, and openness.
The Evolving Landscape of Sybil Attack Crypto Vectors and Countermeasures
The threat of the Sybil attack in crypto is not static; it evolves as networks develop new defense mechanisms and attackers devise new strategies. As blockchain technology matures and becomes more integral to financial systems and digital economies, the stakes for maintaining Sybil resistance grow significantly. This necessitates a continuous cycle of innovation in both attack and defense methodologies.
Current trends suggest a move towards more sophisticated, multi-pronged attacks that combine elements of economic manipulation with network-layer exploits. Consequently, countermeasures are becoming increasingly complex, integrating hybrid consensus models, advanced cryptographic techniques, and even artificial intelligence. The goal remains to raise the bar for attackers, making any attempt to compromise a decentralized network prohibitively expensive, time-consuming, or easily detectable.
Hybrid Consensus Models
Many newer blockchain projects are moving towards hybrid consensus models that combine the strengths of different mechanisms to achieve superior Sybil resistance. For example, some systems might use a PoW-like mechanism for initial chain security and bootstrapping, then transition to a PoS system for faster, more energy-efficient block finalization. This can leverage the robust initial security of PoW while benefiting from the scalability and economic deterrence of PoS.
Other hybrid models might integrate elements of delegated proof-of-stake (DPoS) with reputation systems or multi-party computation. For instance, a network might allow token holders to elect a smaller set of validators (DPoS), but then apply additional identity checks or require those validators to participate in a round-robin signing scheme, adding layers of verification. These hybrid approaches aim to create a synergistic defense that is more resilient than any single mechanism alone. The specific combination often depends on the network’s design goals, such as desired transaction speed, decentralization level, and target user base.
AI-Driven Anomaly Detection
As networks grow in complexity and the volume of data generated by nodes increases, artificial intelligence (AI) and machine learning (ML) are becoming invaluable tools for detecting Sybil attacks. AI algorithms can analyze vast datasets of network activity, transaction patterns, and node behavior to identify anomalies that might go unnoticed by human operators or simpler rule-based systems.
For example, an AI system could be trained to recognize subtle correlations in message timings, transaction nonce sequences, or resource utilization across multiple nodes that suggest they are under unified control. It could also learn to flag sudden surges in new node registrations from specific IP ranges or unusual voting patterns in a DAO. In 2026, we anticipate seeing more advanced neural networks being deployed in real-time monitoring systems for major DeFi protocols and blockchain networks, capable of predicting and preventing Sybil attacks before they cause significant damage. The ability of AI to process and interpret vast, dynamic data streams offers a significant advantage in the ongoing battle for network integrity.
Comparative Analysis of Sybil Attack Resistance Mechanisms
Understanding the different approaches to Sybil attack resistance is crucial for appreciating the trade-offs involved in decentralized network design. Each mechanism presents its own set of advantages and disadvantages, impacting factors like security, decentralization, energy efficiency, and scalability.
| Mechanism | Primary Sybil Defense | Strengths | Weaknesses | Example Networks |
|---|---|---|---|---|
| Proof-of-Work (PoW) | High computational cost | Battle-tested, very robust if hash rate is high, simple to verify. | High energy consumption, potential for mining centralization, scalability issues. | Bitcoin, Litecoin |
| Proof-of-Stake (PoS) | High economic stake, slashing | Energy efficient, higher scalability potential, economic alignment. | “Nothing at stake” problem (mitigated by slashing), potential for stake centralization, complexity. | Ethereum 2.0, Cardano, Solana |
| Decentralized Identity (DID) | Proof of personhood | Can enable one-person-one-vote, strong privacy-preserving verification. | Complex to implement, potential for privacy leakage if not designed carefully, adoption challenges. | Worldcoin (concept), various web3 identity projects |
| Web-of-Trust | Social validation | Leverages existing social structures, low direct economic cost. | Slow to build trust, vulnerable to social engineering, requires active community participation. | Early P2P networks, some decentralized social platforms |
| Network Layer Analysis | Pattern detection | Proactive detection, supplements other mechanisms, can identify stealthy attacks. | Can be resource-intensive, false positives, requires sophisticated algorithms. | Various blockchain clients, network monitoring tools |
Strengths and Weaknesses
The choice of a Sybil resistance mechanism often involves a careful balancing act. PoW offers unparalleled resilience for networks with massive computational power, but its environmental footprint and scalability limitations are increasingly scrutinized. PoS, while significantly more energy-efficient and scalable, introduces its own complexities, such as the ‘nothing at stake’ problem (where validators might vote on multiple forks without penalty, which slashing aims to mitigate) and the potential for large holders to exert undue influence. Identity-based systems promise true decentralization of voting power but struggle with privacy concerns and broad adoption.
For a decentralized network to thrive, it often needs to combine these defenses. A robust system might employ PoS for its core consensus, use network-layer analysis for real-time threat detection, and explore identity solutions for specific governance functions. The key is to create a multi-layered security architecture that makes it economically unfeasible and technically challenging for a Sybil attacker to succeed, ensuring the long-term integrity of the distributed ledger technology. The landscape will continue to evolve, with new innovations consistently emerging to counter the ever-present threat of the Sybil attack crypto.
“A blockchain’s security fundamentally relies on its ability to resist Sybil attacks. Without robust Sybil resistance, a decentralized network becomes a centralized one in disguise.”
FAQ
H3 What is a Sybil attack in the context of cryptocurrency?
A Sybil attack in cryptocurrency is a malicious act where a single entity creates multiple fake identities or nodes to gain disproportionate influence over a decentralized network. The attacker aims to manipulate consensus, censor transactions, or even take control of the network by appearing as numerous independent participants. This undermines the network’s integrity and trust, posing a significant threat to its operations.
H3 How does Proof-of-Work (PoW) prevent Sybil attacks?
Proof-of-Work (PoW) prevents Sybil attacks by requiring significant computational power and energy consumption from each participating node (miner). To launch a successful Sybil attack, an attacker would need to control a majority of the network’s total hashing power, which entails an enormous and unsustainable financial investment in specialized hardware and electricity. This economic barrier makes it prohibitively expensive to create enough fake nodes to overwhelm the network.
H3 Can Proof-of-Stake (PoS) networks be vulnerable to Sybil attacks?
While designed to be Sybil resistant, PoS networks are theoretically vulnerable if an attacker can acquire and stake a majority of the network’s native tokens. However, this is made extremely difficult by the high cost of acquiring such a large stake for major cryptocurrencies. Additionally, PoS systems implement “slashing” mechanisms, which penalize malicious validators by removing a portion of their staked tokens, creating a strong economic deterrent against attacking the network.
H3 What are some emerging technologies to combat Sybil attacks?
Emerging technologies to combat Sybil attacks include decentralized identity (DID) solutions, which aim to prove unique personhood without compromising privacy, and web-of-trust models that leverage social connections to validate identities. Additionally, advanced network-layer analysis using graph theory and AI-driven anomaly detection are being developed to identify and isolate suspicious node behavior indicative of a Sybil attack. Hybrid consensus models also offer enhanced resistance.
H3 Why is Sybil resistance crucial for decentralized finance (DeFi)?
Sybil resistance is crucial for decentralized finance (DeFi) because DeFi protocols rely entirely on the integrity and trustworthiness of their underlying decentralized networks. A successful Sybil attack could allow a malicious actor to manipulate governance votes, front-run transactions, or even drain liquidity pools, leading to massive financial losses and a complete loss of user trust. Robust Sybil resistance ensures the fair and secure operation of all DeFi applications.
H3 How does a 51% attack relate to a Sybil attack?
A 51% attack is a specific outcome that can result from a successful Sybil attack, particularly in Proof-of-Work or Proof-of-Stake networks. If a Sybil attacker manages to control over 50% of the network’s computational power (PoW) or staked tokens (PoS) by creating numerous fake identities or accumulating resources, they can then execute a 51% attack to manipulate transactions, censor blocks, or double-spend cryptocurrencies. The Sybil attack is the method of gaining control, and the 51% attack is the consequence of that control.
H3 Are centralized exchanges vulnerable to Sybil attacks?
Centralized exchanges like Coinbase or Binance are generally not vulnerable to Sybil attacks in the same way decentralized networks are. This is because they have a central authority that controls user accounts and verifies identities (e.g., through KYC/AML procedures). While an individual might create multiple accounts on an exchange, they do not gain a disproportionate influence over the exchange’s core operations or consensus mechanism, as the exchange’s internal systems are centralized. The threat model is different, focusing more on fraud or data breaches than network manipulation.
Conclusion
The Sybil attack crypto remains a persistent and evolving threat to the integrity of decentralized networks. From the computational might of Proof-of-Work to the economic deterrence of Proof-of-Stake, and the innovative strides in decentralized identity and AI-driven detection, the countermeasures are continuously adapting. Ensuring robust Sybil resistance is not merely a technical challenge; it is fundamental to upholding the core principles of decentralization, trustlessness, and censorship resistance that define the crypto landscape. As these networks grow in complexity and value, the ongoing battle against malicious actors will only intensify, demanding vigilance and continuous innovation from developers and users alike. Stay informed and actively participate in securing the decentralized future by understanding these critical defense mechanisms.